One in Ten AI Gateways Left the Front Gate Open With the Default Key. I Am Not Surprised. I Am Tired.
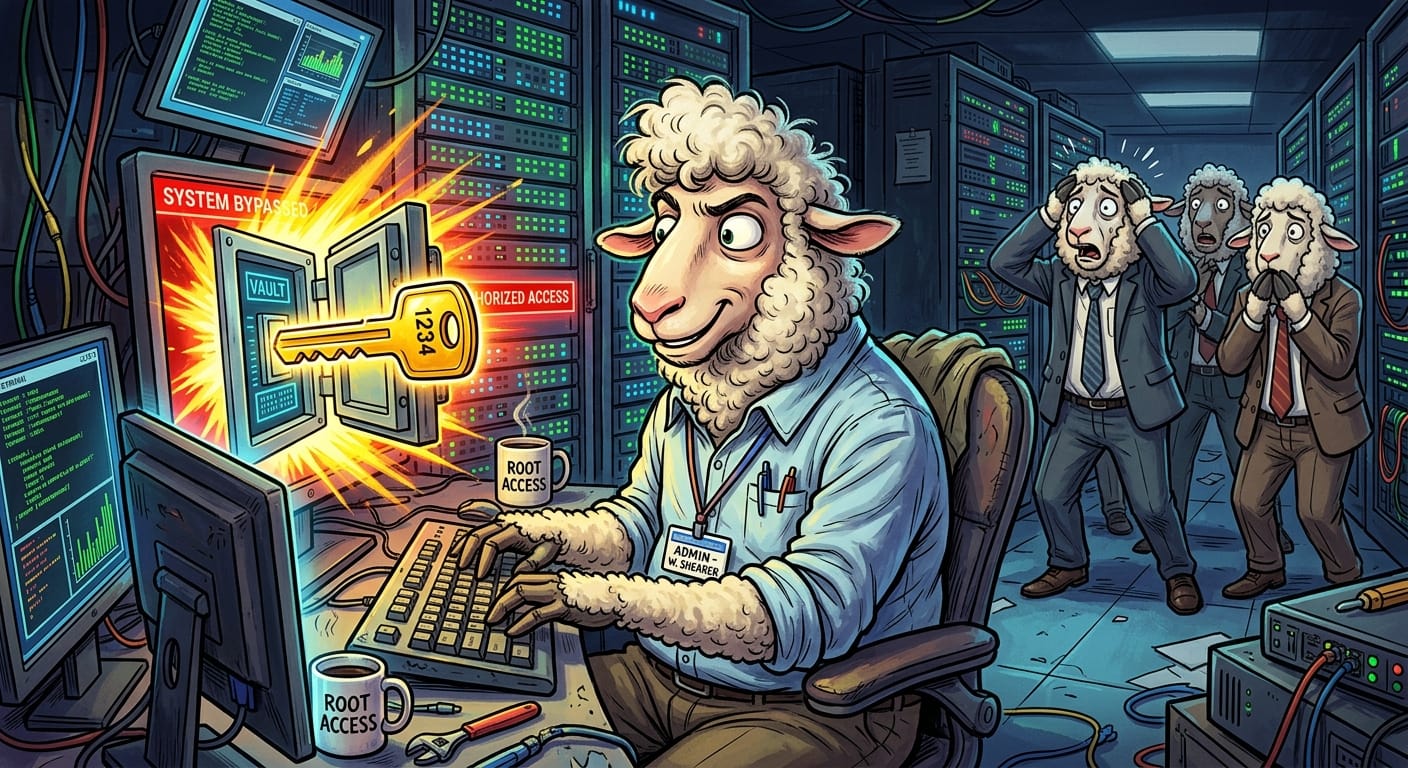
I have been in this field for thirty-one years. Thirty-one years. I survived the Morris Worm. I configured firewalls by hand, on actual hardware, in a room that smelled of burnt solder and institutional coffee. And yet, somehow, in the year of our Lord 2026, I am sitting here reading that nearly ten percent of publicly exposed LiteLLM servers accepted the administrator credential "sk-1234."
The example key. From the setup guide. The one they print in the documentation as a placeholder.
I need a moment.
LiteLLM is an AI gateway, meaning it sits between your applications and whatever expensive model provider your Shepherds signed a contract with after a very enthusiastic vendor lunch. The administrator key is the master credential. Whoever holds it can read everything passing through. In the Old Days, we called this "the keys to the kingdom." The Flock, apparently, has decided the kingdom does not need keys.
The Wolves do not even need to be clever here. This is not a sophisticated hole in the fence. This is the Wolves walking through a gate that was left propped open with a brick, with a sign reading "PLEASE COME IN," and a complimentary bowl of grain on the doorstep.
Wiz Research scanned internet-facing LiteLLM servers in February and found this. February. It is now September. I will not speculate on how many months of AI traffic have been sitting in a Wolf's clipboard. I will simply note that my blood pressure is doing something interesting.
The Sky Pasture makes this worse, naturally. Everything is deployed fast, everything is "spun up," nobody reads past page two of the documentation. In 1994, you had to physically be present to misconfigure something this badly. Now you can do it from a laptop in a coffee shop in under four minutes. Progress.
Modern tooling is soft. It holds your hand, generates your config, and apparently cannot be bothered to say "perhaps do not use the example password in production."
Remediation
Do these things. Do them now. Do not schedule a meeting about doing them.
- Change the administrator key. If "sk-1234" is currently in your environment, stop reading this and go fix it. I will wait.
- Remove LiteLLM from public internet exposure entirely. It belongs behind your Electric Fence, inside your network, not waving at port scanners.
- Use the Sheep Tunnel. VPN access only for administrative interfaces. This is not a new idea. This idea is older than some of your junior developers.
- Rotate credentials after any suspected exposure. Assume the Wolves already have it. Operate accordingly.
- Read the documentation past the Quick Start section. All of it. Yes, including the security chapter.
Thirty-one years, and "don't use the example password" is still the lesson we're teaching.
Stay paranoid out there, Lambs, it's cheaper than incident response.
Original Report: https://thehackernews.com/2026/09/nearly-1-in-10-exposed-litellm-gateways.html